Organizer

Partner Company

Fudan University
Since Windows Vista, TrustedInstaller has served as a privileged core of the Windows servicing stack, supporting system updates, feature management, component repair, and the protection of critical files and registry state. Despite its extensive privileges, its internal architecture and security boundaries have received limited public analysis.
In this talk, we present what we believe is the first end-to-end public analysis of TrustedInstaller. We uncover its undocumented architecture, execution model, and trust boundaries across the Windows servicing stack. We also show how cross-component reverse engineering enabled us to connect fragmented evidence across multiple binaries and identify previously hidden attack surfaces.
Building on this analysis, we disclose a previously unknown local privilege-escalation vulnerability, CVE-2026-61938, a use-after-free vulnerability in the TrustedInstaller service that can lead to SYSTEM privileges. Beyond this vulnerability, we introduce TrustFall, another new attack technique that turns previously unreported attack surfaces in TrustedInstaller into a powerful primitive for local privilege escalation under default Windows configurations. We will demonstrate TrustFall and its security implications during the talk.
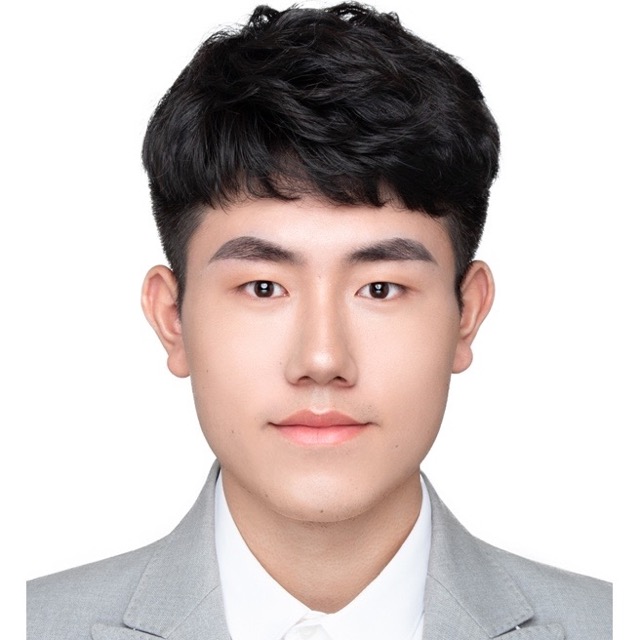
Bocheng Xiang (@crispr_x) is a PhD at Fudan University. He is listed on the MSRC MVR 2024/2025 and ranked Top #20 on the MSRC 2024 Q3 Windows Leaderboard. He has published papers at USENIX Security,CCS and NDSS, and his works have been shared at PoC2025 and Black Hat USA/Europe and DEF CON 24.
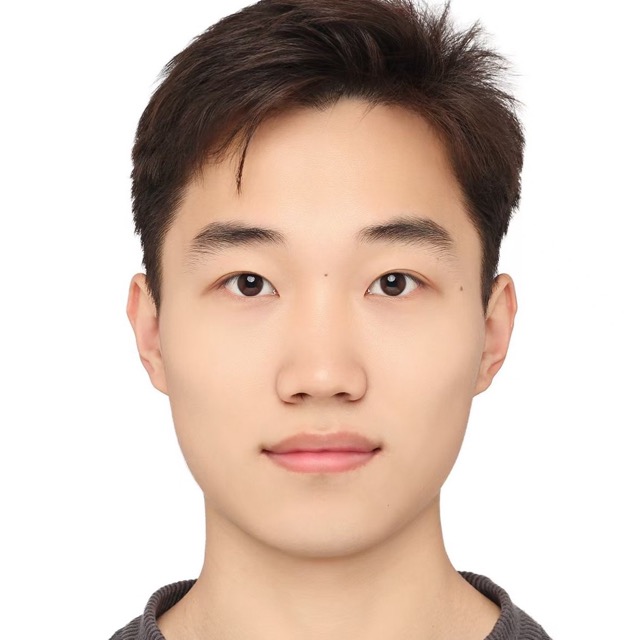
Hao Huang (@h4urek) is a master student at Fudan University. He is listed on the MSRC MVR 2026.He has published papers at USENIX Security,CCS and NDSS.