Abstract
Fuzzing is a powerful technique for identifying vulnerabilities in software. This hands-on training will cover the theory and practical aspects of fuzzing, including coverage-guided fuzzing, basic blocks and binary instrumentation, corpus collection and minimization, target selection, crash triage and root cause analysis, and real-life CVE analysis. Attendees will have the opportunity to practice fuzzing on Linux and apply the concepts and techniques learned in the training to fuzz real world software. This training is suitable for attendees with a basic understanding of software development and testing and is beginner friendly.
This training will start from user mode fuzzing and later on covers topics like linux kernel fuzzing and firmware fuzzing etc.
In this training, attendees will also learn about the different types of vulnerabilities that can be found through fuzzing, including buffer overflows, heap overflows, integer overflows, use-after-free errors, and out-of-bounds read/write errors. We will discuss the underlying causes and potential impacts of these vulnerabilities, as well as how to identify and address them through fuzzing. In addition to coverage-guided fuzzing, we will also introduce other types of fuzzer, such as dumb fuzzers and mutation fuzzers, and discuss their benefits and limitations. Attendees will also learn how to use tools such as GDB and Crashwalk to debug and analyze crashes, and to perform root cause analysis to identify the underlying cause of vulnerabilities.
Trainer Info
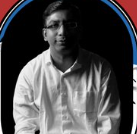
Hardik Shah (@hardik05) is an experienced cyber security professional with 17+ years of experience in the computer security industry. Currently works as a Principal Security Researcher at Vehere where he is responsible for analysing latest threats, detecting them and product improvements. In the past he has worked with various security companies like Sophos, McAfee, and Symantec, where he has built research teams from ground zero, managed various critical cyber threats to provide protection to customers, implemented various product features and has mentored many people.
Hardik is also known for his skills in fuzzing and vulnerability discovery and analysis. He has discovered 50+ vulnerabilities in Microsoft and various open source software. He had conducted workshops at various industry leading cyber security conferences such as Defcon, Bsides, RSA dark arts, and many others. Hardik enjoys analysing latest threats and figuring out ways to protect customers from them.


 /var/www/html/templates/v1/inner-section/sponsors.php on line 35
 /var/www/html/templates/v1/inner-section/sponsors.php on line 35
 /var/www/html/templates/v1/inner-section/sponsors.php on line 35
 /var/www/html/templates/v1/inner-section/sponsors.php on line 35
 /var/www/html/templates/v1/inner-section/sponsors.php on line 35
 /var/www/html/templates/v1/inner-section/sponsors.php on line 35
 /var/www/html/templates/v1/inner-section/sponsors.php on line 35
 /var/www/html/templates/v1/inner-section/sponsors.php on line 35